Why customers choose Tenable over CrowdStrike
VUE UNIFIÉE
VUE UNIFIÉE
Tenable One Exposure Management platform continuously evaluates the accessibility, exploitability, and criticality of all your digital assets across cloud and on-prem: IT systems, cloud resources, identity systems, web apps, OT devices, external attack surface management (EASM) and third-party cybersecurity tools.
- See all of your exposures in a unified view
- Pull in multiple diverse vulnerability sources, including threat intelligence data like CrowdStrike
“CrowdStrike’s platform requires you to have an additional logging aggregator or platform that would ingest the logs from their identity protection platform. Tenable’s Identity Exposure [part of Tenable One] fits nicely into our ecosystem… Tenable One will have visibility into configuration issues in our Active Directory [AD] or authentication mechanisms... It just brings it nicely together.”
Director Cybersecurity, NA Health Research Company1
Unified analytics
Unified analytics
Separate actual exposures from all the noise to enhance productivity and minimize risk:
- Tenable offers fully integrated and normalized risk metrics for all asset types and data sources.
- Tenable maps all assets, identities, and risks to critical business services, processes and functions for rich context to drive smarter remediation decisions.
- The addition of 3rd party data, including threat intelligence sources like CrowdStrike intelligence, centralizes the view and improves context-driven risk prioritization

Security endpoint
La sécurité au-delà du point de terminaison
- Continuous assessments across IT, cloud, OT/IoT, networks and third-party apps.
- Detect lesser-known CVEs and systems missing EDR agents.
- Use multiple detection technologies: agents, passive monitoring, distributed scan engines, dynamic application security testing (DAST), OT sensor, and infrastructure as code (IaC) assessment.
- Analyze data and context from multiple third-party sources.
Data accuracy
Data accuracy and transparency
- Tenable’s rich plugin output provides detailed vulnerability context to streamline dispute resolutions and minimize time wasted on false positives.
- Unlike CrowdStrike, which primarily relies on package enumerations, Tenable performs additional checks, like examining dynamic link library (DLL) files and registry keys for more accurate detection and fewer false positives.
- Tenable’s Vulnerability Intelligence tracks vulnerability history over time. Exposure Response enables risk remediation tracking with service level agreements (SLAs). Together, they create a unified risk-based workflow, regardless of patch availability.
“CrowdStrike…has a vulnerability management module…we own that module, but frankly, it doesn't have the same coverage as the other enterprise vulnerability management tools such as Tenable…Tenable by far has better vulnerability coverage, meaning they assess way more applications and way more vulnerabilities.”
Security Manager, Optical retail company4
Compliance leader
Leader en termes de conformité
Tenable covers a wide variety of compliance frameworks across operating systems to help ensure compliance across your complex and diverse ecosystems.

Compare Tenable One Exposure Management to CrowdStrike Falcon Exposure Management

|

|
|
|---|---|---|
|
Tenable
Included: Unified exposure across IT, cloud, identity, and OT
|
Core focus
|
CrowdStrike
Not included: Exposure from endpoint and identity telemetry
|
|
Tenable
Included: Combines integrated metrics across risk-based vulnerability management, web app scanning (WAS), cloud security, identity exposure, OT security, EASM, and third-party data
|
Analyses de gestion de l'exposition
|
CrowdStrike
Not included:
Lacks comprehensive network scanning, web app security (WAS), identity data, and holistic context beyond endpoints No Cyber Exposure Score and equivalent board-level risk metric |
|
Tenable
Included: Unified asset graph across IT, cloud, OT, and identities
|
Inventaire des assets
|
CrowdStrike
Not included: Based on discovered external and managed endpoint assets
|
|
Tenable
Included: Exposure Response to track risk remediation with SLAs — instead of cumulative risk scores — a single end-to-end workflow, and a risk-based approach, regardless of patch availability
|
Réponse aux expositions
|
CrowdStrike
Not included: Non fourni
|
|
Tenable
Included: Covers a wide variety of compliance frameworks across various OSs
|
Conformité
|
CrowdStrike
Not included: Limited support for CIS and basic DISA STIGs
|
|
Tenable
Included: Industry’s broadest coverage published on https://www.tenable.com/plugins
|
Couverture des vulnérabilités
|
CrowdStrike
Not included: Non communiqué
|
|
Tenable
Included: Comparison of cyber risk to industry peers and to quickly identify shortcomings and strengths
|
Comparaison à d'autres entreprises du secteur
|
CrowdStrike
Not included: Non fourni
|
|
Tenable
Included: Coverage for a wide variety of asset types — endpoints, network devices, OT, cloud workloads, web apps
|
Coverage scope
|
CrowdStrike
Not included: Primarily focused on endpoints with a Falcon agent and network devices visible to a Falcon agent
|
|
Tenable
Included: Agent-based, agentless, and network scanning
|
Scanning technology
|
CrowdStrike
Not included: Agent-based and network scanning for devices visible to a Falcon agent
|
|
Tenable
Included: High—replaces scanners, CSPM, IAM risk tools, attack graphing, custom dashboards
|
Tool consolidation potential
|
CrowdStrike
Not included: Low—adds exposure context to Falcon but doesn’t replace core security tools
|
|
Tenable
Included: Deep file interrogation and registry checks
|
Vulnerability depth
|
CrowdStrike
Not included: Agent looks at the installed OSs and apps
|
|
Tenable
Included: Cross-OS patch management with SLA tracking and rollback, fully integrated into the platform - powered by HexaAI, agentic AI engine
|
Closed-loop remediation
|
CrowdStrike
Not included: Remediation requires a separately configured third-party tool
|
|
Tenable
Included: The only open-source community where security practitioners can discover, share and collaborate on AI components, including agents, skills, MCP servers and playbooks.
|
CrowdStrike
Not included: Lives behind the paywall, available only to CrowdStrike engineers and selected SI partners
|
1 - Internal customer interview
2 - Falcon Exposure Management Datasheet
3 - CrowdStrike’s announcement
Désigné comme un leader en gestion de l'exposition par des analystes du secteur
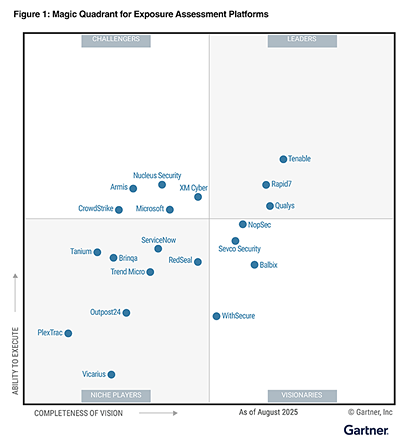
Tenable désigné leader dans le « 2025 Gartner® Magic Quadrant™️for Exposure Assessment Platforms (EAP) »
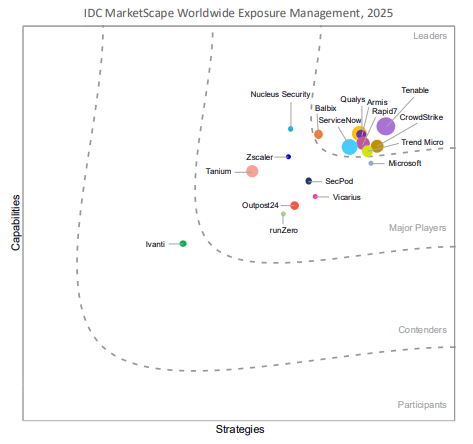
Tenable One
Demander une démo
La plateforme de gestion de l'exposition alimentée par l'IA leader du secteur
Merci
Nous vous remercions de votre intérêt pour Tenable One.
Un représentant vous contactera prochainement.
Form ID: 7469
Form Name: one-eval
Form Class: c-form form-panel__global-form c-form--mkto js-mkto-no-css js-form-hanging-label c-form--hide-comments
Form Wrapper ID: one-eval-form-wrapper
Confirmation Class: one-eval-confirmform-modal
Simulate Success